-
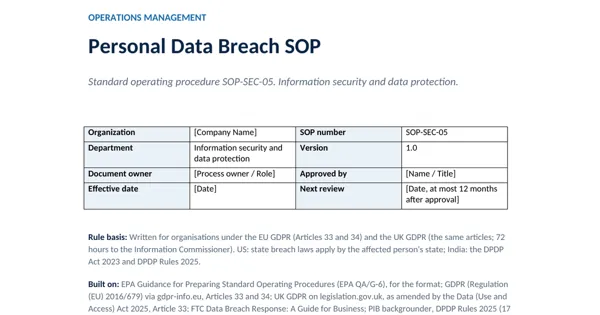 Word document preview
Information Security SOPs
Personal Data Breach SOP
3 downloads per free account, no card needed.
Who this is for
A spreadsheet of customer data went to the wrong person and the managing director asks whether you must tell the regulator, by when and who writes the notice.
What is inside
- 21 numbered steps in 5 stages, each with one owner, a record and a timing
- A timing on every step, from the recorded awareness time to the 72-hour regulator deadline
- Risk scale (none, risk, high risk) that decides regulator and individual notices
- Notice content lists for the supervisory authority and for affected people
- Country table: EU, UK, US state laws, India DPDP Rules, with what to check
- Breach register entry for every breach, reported or not, as GDPR Article 33(5) requires
How to use it: Name your data protection lead and deputy, enter your supervisory authority and its reporting link, and confirm which countries' rules apply; rehearse it once a year.
Files & formats
- DOCXpersonal-data-breach-sop.docx42 KB
Opens in Microsoft Word or Excel, Google Docs or Sheets and LibreOffice. Delivered instantly from your browser.
Free downloads & full access
Every account gets 3 free downloads. Re-downloading a file you already have does not count. This one on its own is $12.99, and buying it keeps your free downloads for something else. Full access is a one-time $249 for all 300 SOPs and the SOP writing kit, for life.
Bought with a different email? Open your account and enter your order number.
Licence
Use and adapt the document inside your own organisation or for your own clients. Do not resell or republish the SOPs themselves. The SOP does not give certification or legal compliance on its own. These SOPs are original working documents built on the public law and guidance named here. They are not legal, safety or compliance advice, are not endorsed by its publisher and do not give compliance on their own. Rules change: check the current official text.