-
 Word document preview
Information Security SOPs
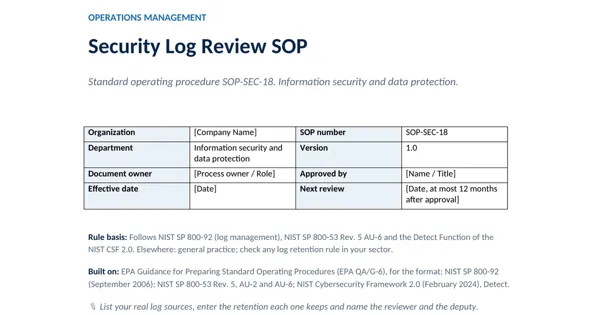
Security Log Review SOP
3 downloads per free account, no card needed.
Who this is for
An auditor asks to see evidence that someone looks at the security logs, and the logs exist but nobody reads them.
What is inside
- 18 numbered steps in 4 stages: daily, weekly, monthly, follow-up
- Log source table: 7 sources with what to look for and how often
- Steps that check log collection is working before reading the logs
- Escalation to the security incident SOP with the log extract preserved
- Review record signed for each check, even when nothing was found
- Basis: NIST SP 800-92 log management and CSF 2.0 Detect
How to use it: List your real log sources, enter the retention each one keeps and name the reviewer and the deputy.
Files & formats
- DOCXsecurity-log-review-sop.docx41 KB
Opens in Microsoft Word or Excel, Google Docs or Sheets and LibreOffice. Delivered instantly from your browser.
Free downloads & full access
Every account gets 3 free downloads. Re-downloading a file you already have does not count. This one on its own is $12.99, and buying it keeps your free downloads for something else. Full access is a one-time $249 for all 300 SOPs and the SOP writing kit, for life.
Bought with a different email? Open your account and enter your order number.
Licence
Use and adapt the document inside your own organisation or for your own clients. Do not resell or republish the SOPs themselves. The SOP does not give certification or legal compliance on its own. These SOPs are original working documents built on the public law and guidance named here. They are not legal, safety or compliance advice, are not endorsed by its publisher and do not give compliance on their own. Rules change: check the current official text.