-
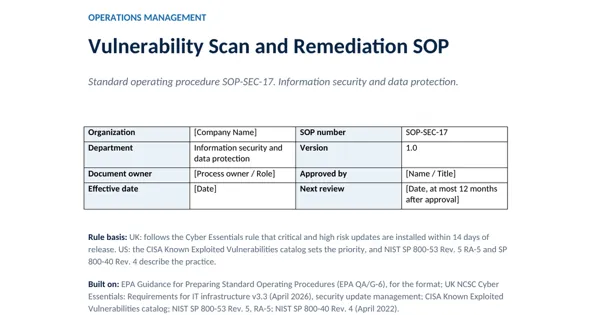 Word document preview
Information Security SOPs
Vulnerability Scan and Remediation SOP
3 downloads per free account, no card needed.
Who this is for
A customer pen test found old issues and the board asks how vulnerabilities are found, who fixes them and how fast.
What is inside
- 19 numbered steps in 4 stages: scan, rate, fix, verify and report
- Remediation table: 4 ratings with target days and who approves a delay
- Cyber Essentials rule on page 1: critical and high risk updates within 14 days of release
- CISA Known Exploited Vulnerabilities check that moves an item to the top
- Risk acceptance record with an end date for anything that cannot be fixed
- Monthly report: open items by age and rating
How to use it: Name your scanner and scan schedule, confirm the target days in the remediation table and who signs a risk acceptance.
Files & formats
- DOCXvulnerability-scan-and-remediation-sop.docx41 KB
Opens in Microsoft Word or Excel, Google Docs or Sheets and LibreOffice. Delivered instantly from your browser.
Free downloads & full access
Every account gets 3 free downloads. Re-downloading a file you already have does not count. This one on its own is $12.99, and buying it keeps your free downloads for something else. Full access is a one-time $249 for all 300 SOPs and the SOP writing kit, for life.
Bought with a different email? Open your account and enter your order number.
Licence
Use and adapt the document inside your own organisation or for your own clients. Do not resell or republish the SOPs themselves. The SOP does not give certification or legal compliance on its own. These SOPs are original working documents built on the public law and guidance named here. They are not legal, safety or compliance advice, are not endorsed by its publisher and do not give compliance on their own. Rules change: check the current official text.